Cyber Intruders Hijack Microsoft’s X Profile to Promote Questionable “Clippy” Token
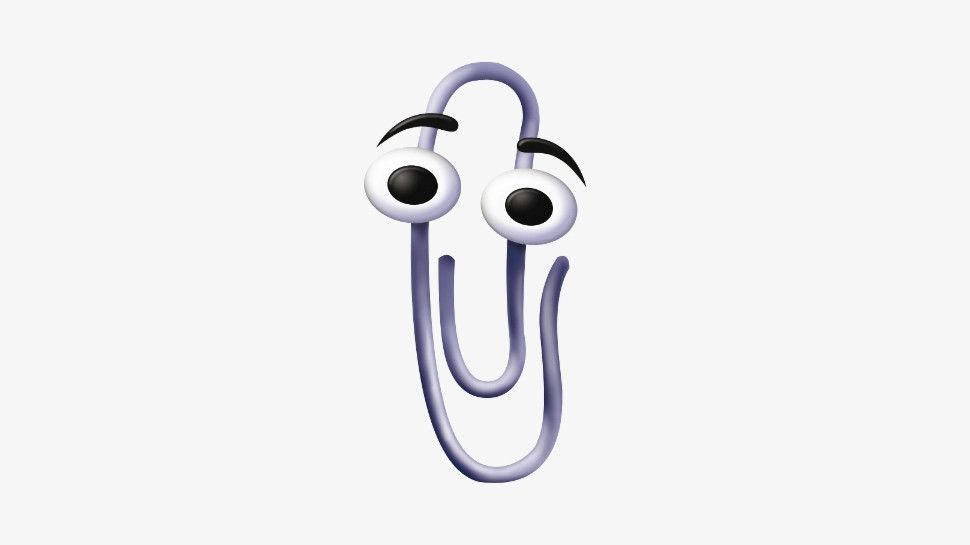
On Tuesday, Microsoft announced that its official X (formerly Twitter) account had been breached, and the perpetrators used it to advertise a freshly launched cryptocurrency called $CLIPPY, which alludes to the firm’s much‑maligned paper‑clip helper.
The hijackers circulated a batch of promotional tweets that imitated Microsoft’s typical tone, even inserting a bogus apology stating the company was “launching an innovative digital asset.” Those messages displayed a logo nearly identical to Microsoft’s own, a ploy intended to give the fraud an air of legitimacy.
Within moments, the counterfeit posts were boosted by retweets and replies from accounts masquerading as Microsoft affiliates, widening the appeal of a rapid‑gain scheme linked to the nostalgic Clippy figure. The pitch touted lofty returns for early backers, echoing the typical bait used in the recent surge of crypto scams across social networks.
Microsoft’s security personnel acted swiftly, verifying that the account was accessed illegitimately. The firm deleted the offending posts, changed the login details, and added extra protective measures to deter future incidents. In a short statement, Microsoft stressed that it does not back any cryptocurrency and urged users to treat unsolicited investment offers with caution.
Security analysts point out that commandeering verified corporate profiles gives scammers a shortcut around usual trust safeguards. By exploiting a recognizable brand and a nostalgic cultural symbol, the perpetrators boosted the chances that users would follow malicious links or buy the token. The episode highlights the persistent difficulties regulators and platforms face as decentralized finance expands rapidly and digital identities become easy to counterfeit.
Investigators have not yet pinpointed the actors responsible for the intrusion, though law‑enforcement bodies are keeping watch for possible financial offenses. In the meantime, security counsel advises users to confirm any crypto‑related news directly with the issuing firm, activate multi‑factor authentication on their social media accounts, and stay wary of proposals that appear overly lucrative.

Comments (0)
Be the first to comment.
Join the discussion